

Listen: the breakdown
Developing story: This story is still unfolding. We are tracking it and will update this article as more details are confirmed.
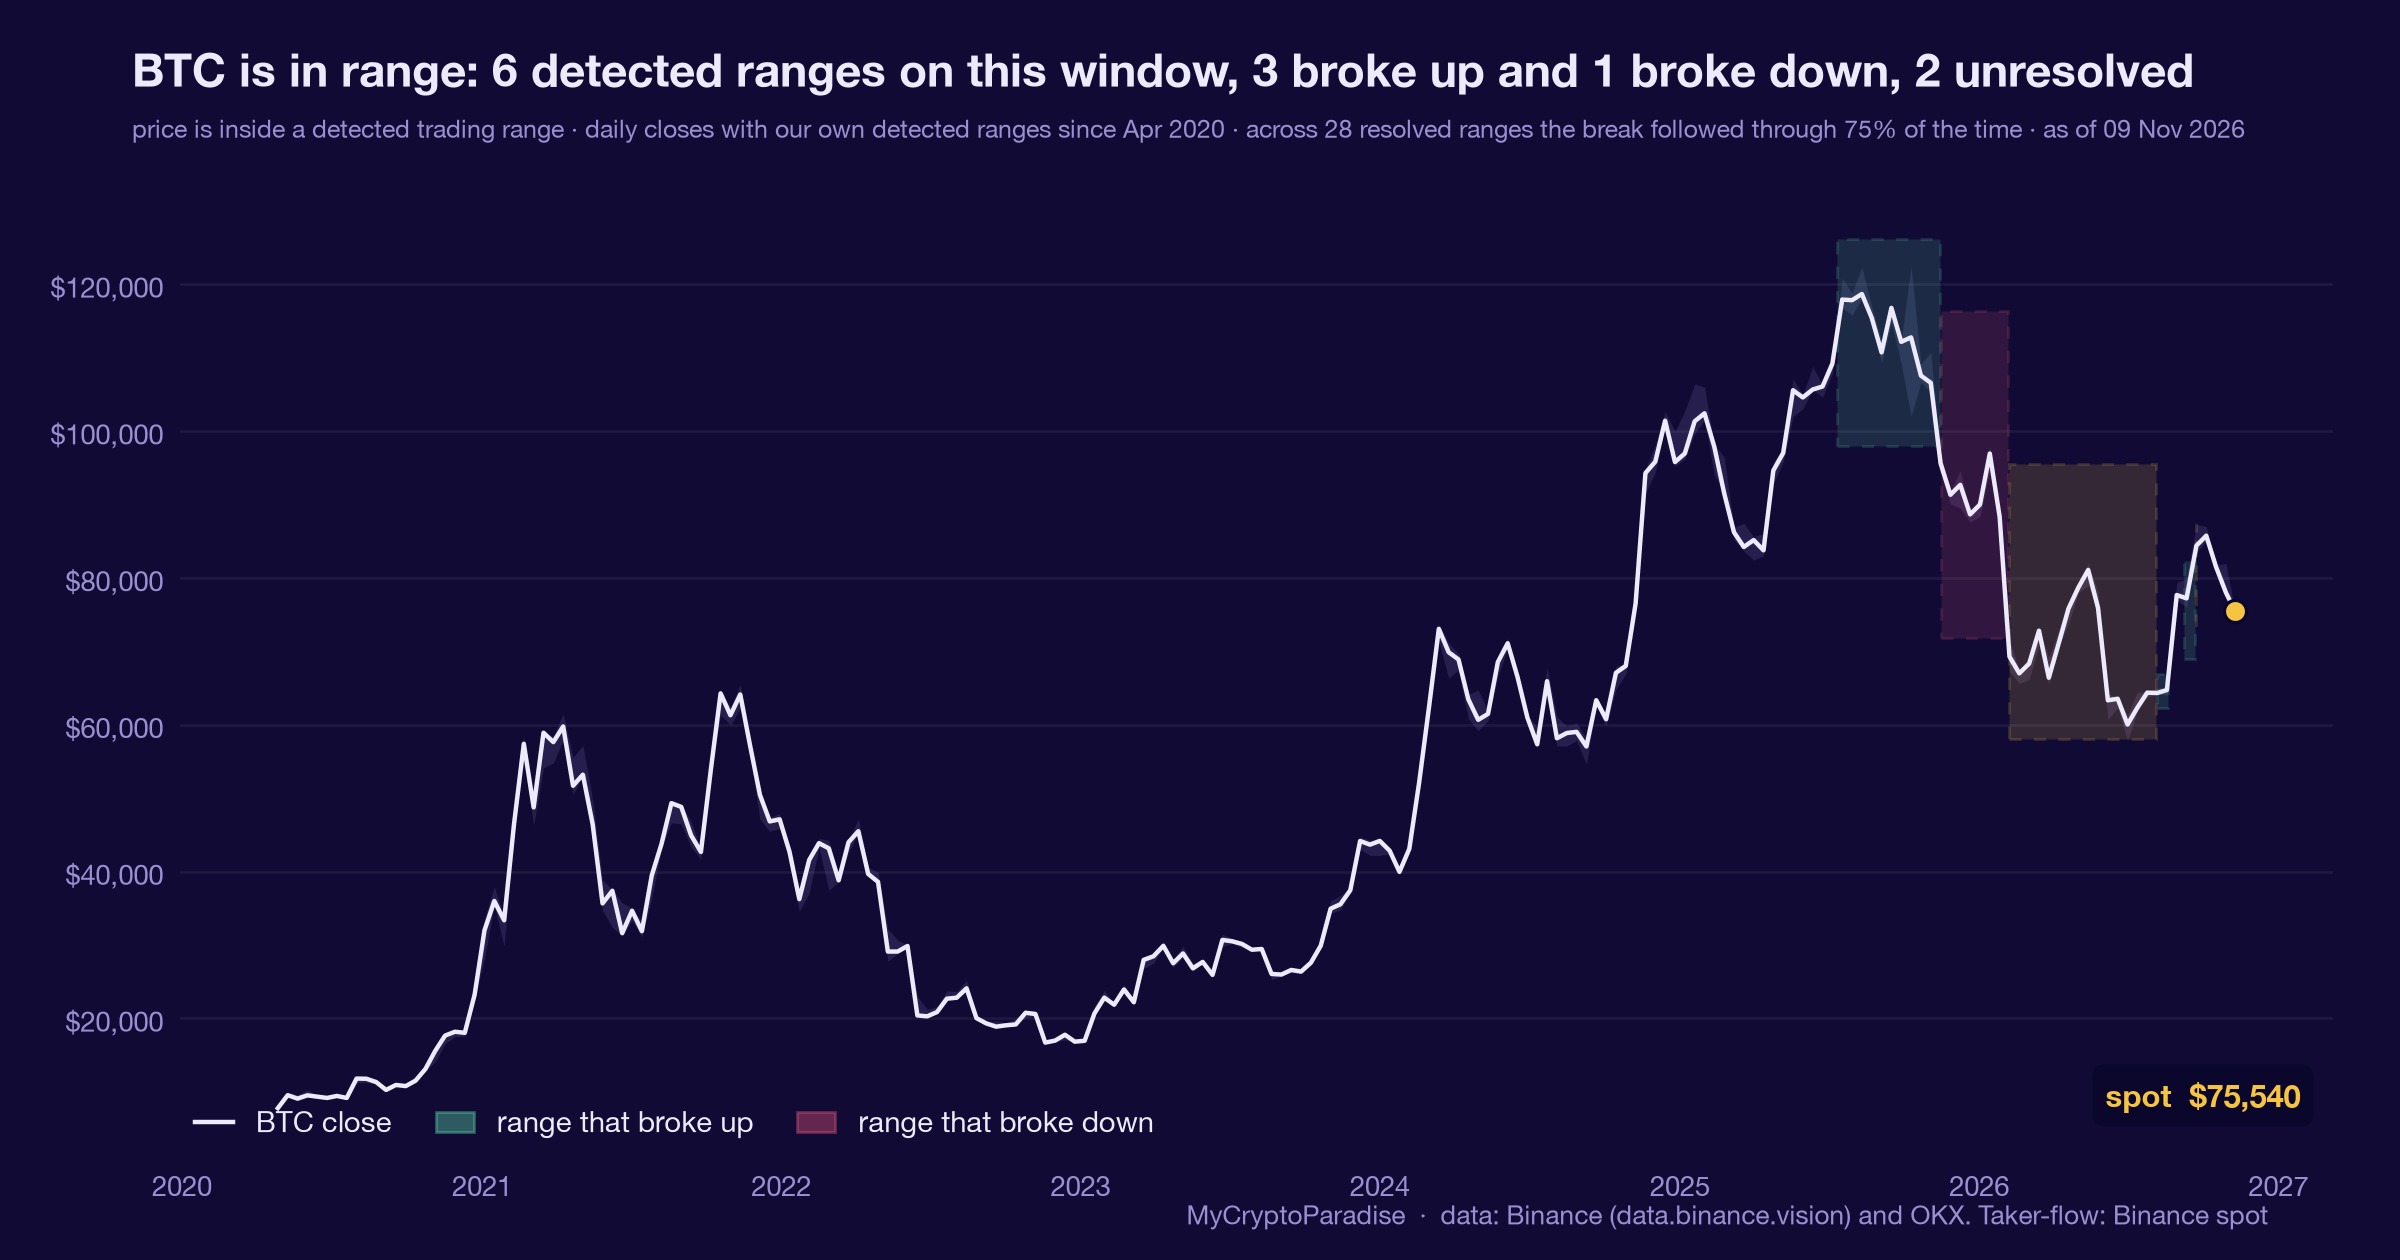
Market briefing: A security alert says Across lost control of its domain to a DNS hijack after social engineering against its registrar. BTC traded near $73,731 as of 04:39 UTC, with no evidenced spillover.
- Across's domain was reportedly hijacked via a DNS attack around 18:45 UTC on November 10
- The attacker allegedly social-engineered registrar Namecheap, not the bridge's smart contracts
- The claim is single-sourced so far, with no evidenced impact on BTC, ETH or alt liquidity
An Across DNS hijack reportedly swapped the bridge's real website for a fake one, without touching a single line of its code. So who really guards the front door?
At roughly 18:45 UTC on November 10, a security alert flagged a DNS hijacking attack against Across. The attacker did not break the bridge's code. They allegedly talked their way past Namecheap, the domain registrar, then seized control of the official Across domain.
Once in control, the attacker replaced the real Across website with their own copy. The smart contracts stayed untouched. The front door simply pointed somewhere else.
This is a social engineering story first and a crypto story second. A bridge can audit its contracts for months. It cannot easily audit a support agent at its registrar taking a convincing phone call.
We have already covered two security incidents today, an accounting-bug exploit and a nine-figure laundering trail. This one differs in kind. No contract was drained here. The attack surface was the domain name itself.
Honesty matters on this one. The claim currently rests on a single security alert. We have not seen independent corroboration in the data we gathered, so treat the specifics as provisional rather than settled.
What is not provisional is the vector. DNS hijacks through registrar social engineering are a known, repeatable attack. They turn a trusted URL into a trap, which means a user who typed the correct address could still land on a hostile site.
For Across users, the immediate risk is phishing. A cloned site can request token approvals or route funds straight to the attacker. The protocol's underlying security is almost beside the point if the page you load is fake.
A phone call beat the smart contracts
The real lesson sits above Across. Bridges pool large amounts of liquidity, which makes their front ends high-value targets. The money lives in audited contracts, but users reach it through a website. Compromise the website and you compromise the on-ramp.
Registrar social engineering is the soft underbelly of this whole model. A domain is only as safe as the humans who can edit its DNS records. That control sits with a registrar's staff, far from any blockchain, and a persuasive caller can undo months of security engineering in minutes.
So the transmission here is deliberately narrow. The driver is a hijacked domain. The direct effect is trust risk for Across users. The downstream effect on broader liquidity, in the data we have, is close to nothing.
That does not make it harmless. Every incident like this chips at the assumption that typing a known URL is safe. Over time, repeated front-end attacks raise the friction of using any bridge, which quietly thins the audience willing to move size across chains.
There is a grim comedy in it too. The industry obsesses over formal verification and multi-million-dollar audits, then gets undone by a phone call to customer support.
For traders, the structural point is simple. The code is rarely the weakest link anymore. The weakest link is the boring infrastructure sitting between you and the contract, and that is exactly what this alert just exposed.
Trust risk stays boxed inside Across
BTC was trading near $73,731 as of 04:39 UTC, down about 1.2% on the day. ETH sat near $2,067, softer by 2.4%, with BNB near $681. None of that softness traces back to Across in the evidence we gathered.
So the honest read on contagion is contained, at least for now. The 24h weakness in ETH and BNB looks like independent, mildly risk-off background, not a downstream effect of this hijack. Both were even flat-to-up on the hour as the alert circulated.
The cleaner way to read it: this is a protocol-specific trust shock, not a liquidity event. There is no large contract loss driving forced selling, no cascade of liquidations tied to the name. The first-order damage is reputational and user-facing.
That still tilts the bridge sector's tone bearish. Front-end attacks make users hesitate, and hesitation is friction. When the on-ramp itself feels unsafe, flows slow before they stop.
For BTC and ETH directly, the knock-on is minimal today. Neither derives its bid from one bridge's domain. The risk is slower and reflexive: enough incidents like this, and cross-chain activity cools, which saps a chunk of demand that eventually reaches the majors.
For now, treat the price action and this story as two separate threads. The drawdown is macro-flavoured. The hijack is a security headline that Across users must act on immediately, even as the wider market barely registers it.
Verify the URL before you bridge
The first thing to watch is corroboration. Right now this sits on one security alert, with no independent confirmation in our data. A matching statement from the protocol's own channels, or the registrar acknowledging the breach, would move this from provisional to confirmed.
The second thing is domain control. A clean resolution looks like the real team regaining the domain, restoring correct DNS records, and publishing a verified safe address. Until that happens, assume the front end cannot be trusted at face value.
Invalidation is just as real a path. If no corroboration appears and the protocol denies any compromise, the story deflates into noise. That outcome is entirely possible with a single-sourced claim, and we will treat it honestly if it lands that way.
For users, the practical checklist does not wait on any of that. Do not reach Across through search results or links in messages. Verify approvals carefully, and revoke any you granted to an unfamiliar contract during the window.
Watch wallets too. If drainer activity tied to a fake Across site shows up on-chain, that corroborates the attack faster than any statement. A quiet chain, by contrast, argues the damage was limited or the claim overstated.
The wider signal to monitor is sector mood. One isolated hijack is a user problem. A run of front-end attacks across bridges would be a theme, and themes are what actually move sentiment and flows.
What a single-sourced alert means here
The ParadiseTeam frames this as headline risk, not a directional thesis. With BTC near $73,731 and no evidenced link to the hijack, there is nothing here that tells us where ETH or BTC go next.
Most important, we see no footprint of smart money positioning around this specific story. Sentiment data came back empty. So any claim that whales are accumulating fear or distributing into it would be invention, and we will not pretend otherwise.
That absence is itself the insight. Our edge usually comes from spotting bearish news land at support while retail panics, which flags accumulation. This story offers no such structure, because it never touched price in the first place.
Our standing caution still applies to the tape, not to Across. The market tone reads mildly risk-off, with the majors soft over 24h. In that environment, strength into resistance can meet sellers, and we respect that regardless of this incident.
For anyone actually using Across, the risk-first read is blunt. Treat the front end as hostile until the domain is verifiably restored, and size any interaction as if your approval could be malicious.
For everyone else, this is a reminder to separate noise from signal. A single-sourced security alert, with no price transmission, is not a reason to flip a bias on BTC or ETH. The level that matters for the majors is being set by macro flows today, not by one bridge's registrar.
Track it live: our Crypto Fear and Greed Index tracks this in real time, so you can watch it play out for yourself.
Related coverage
For exact entries, targets, and stop losses with full risk management, that is what ParadiseFamilyVIP is for. New to reading these moves? Start with our crypto trading strategies guide.
ParadiseTeam is monitoring the market situation closely, and we are taking these developments into consideration while building our trading tactics inside ParadiseFamilyVIP.
Crypto trading involves substantial risk. Prices are volatile and you can lose money. This article is educational and is not financial advice. Past performance does not guarantee future results.
Does the Across domain hijack claim get independently confirmed from here?
How 1 Paradiser is calling it
The first call is still open
Free account, no password. Members just sign in.


Join the discussion
No comments yet. Members, share how you are reading this.